You haven't signed in yet, you can have a better experience after signing in
*Please complete the payment within {{receiveCouponInfo.expire_at}}Previous use*
You haven't signed in yet, you can have a better experience after signing in


Activity Rules
1、Activity time:{{ info.groupon.start_at }} ~ {{ info.groupon.end_at }}。
1、Activity time:cease when sold out。
2、Validity period of the Group Buying:{{ info.groupon.expire_days * 24 }} hours。
3、Number of Group Buying:{{ info.groupon.need_count }}x。
Please Pay Attention
1、Teamwork process: Join/initiate a Group Buying and make a successful payment - Within the validity period, the number of team members meets the activity requirements - Group Buying succeeded!
2、If the number of participants cannot be met within the valid period, the group will fail, and the paid amount will be refunded in the original way.
3、The number of people required and the time of the event may vary among different products. Please pay attention to the rules of the event.
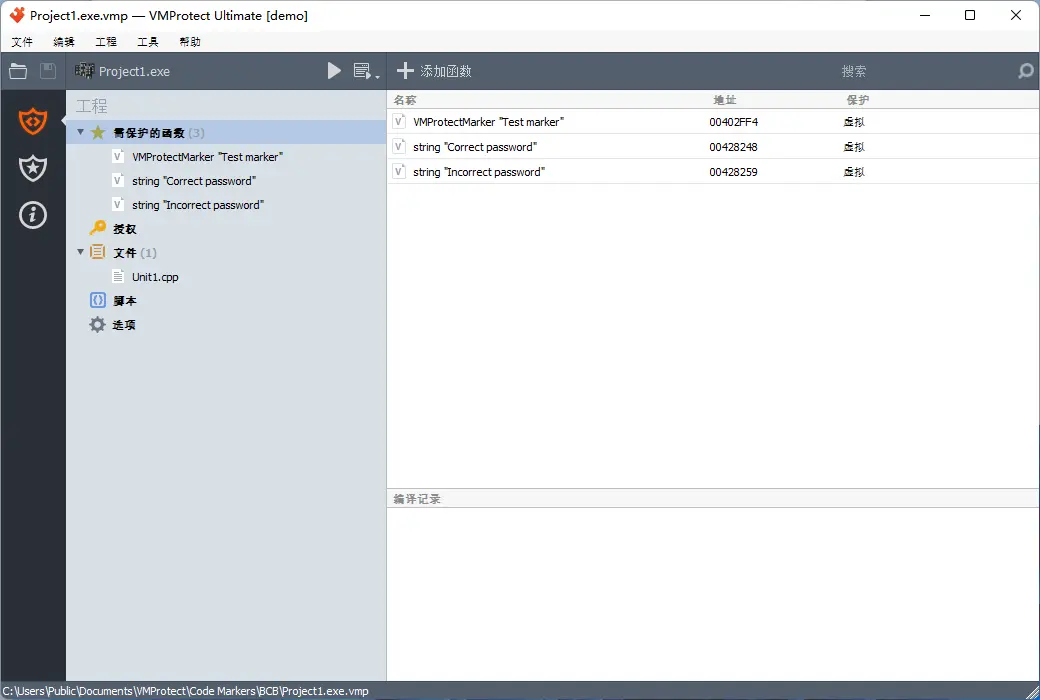
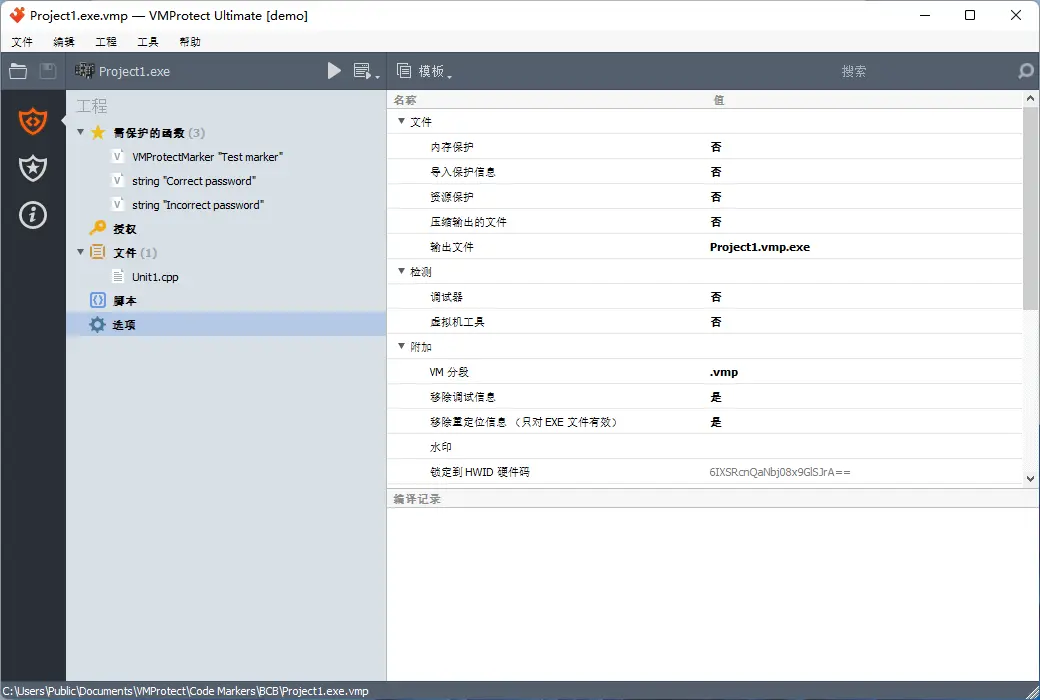
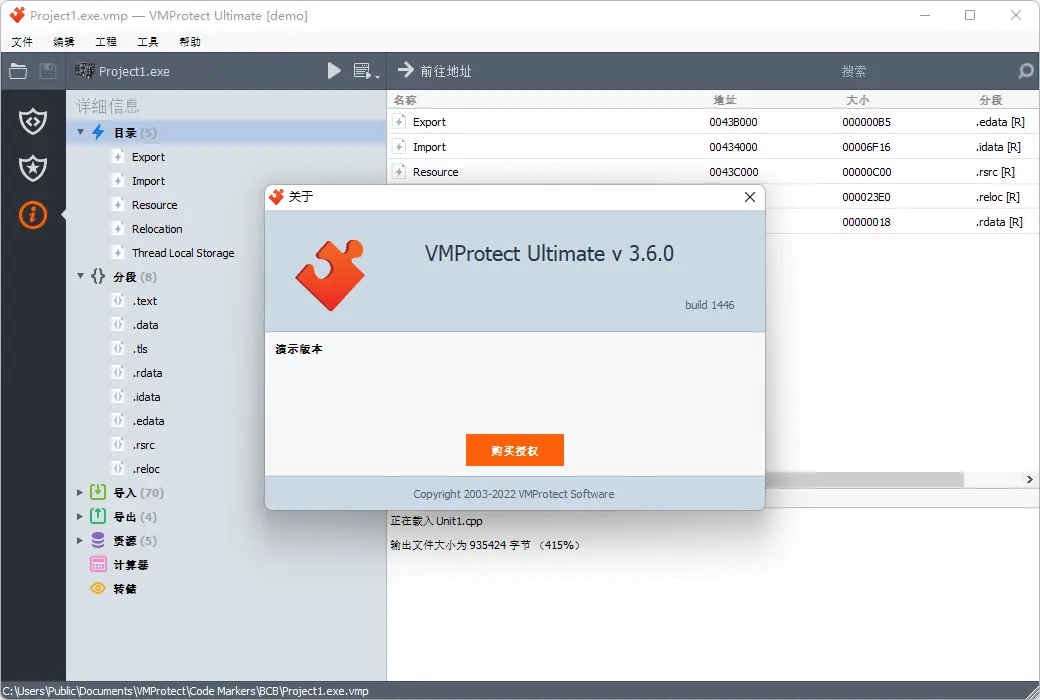
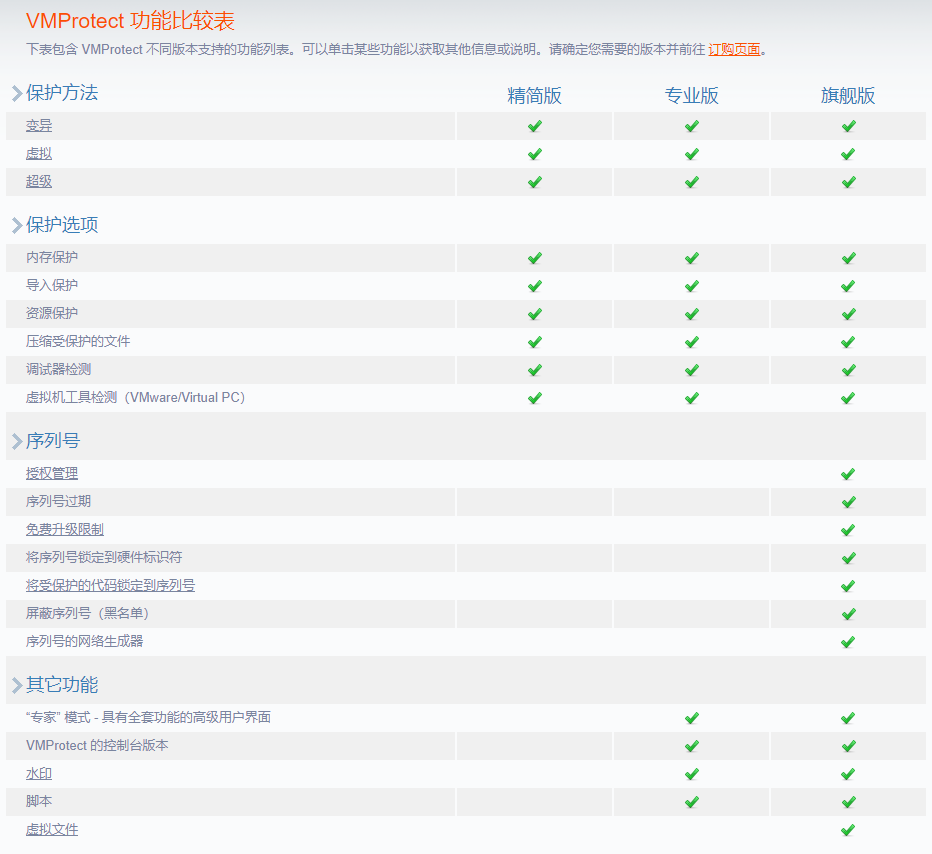
VMProtect protects code by executing it on virtual machines with non-standard architectures, making it extremely difficult to analyze and crack software. In addition, VMProtect can generate and verify serial numbers, restrict free upgrades, and more.
Five reasons to use VMProtect?
Most of our competitors do not have the same innovative features, nor do they have a combination of equally leading features and cost efficiency.
1. VMProtect virtualization code
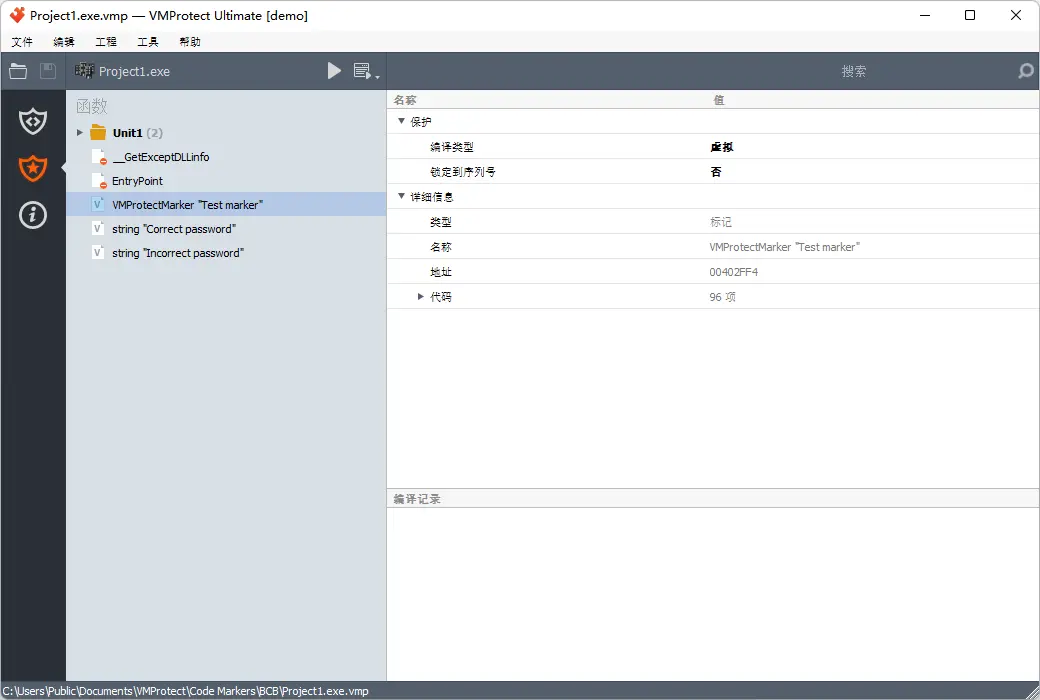
Code virtualization is the next step in software protection. Most protection systems encrypt code and then decrypt it at the start of the application. VMProtect doesn't even decrypt code! Instead, encrypted code runs on a virtual CPU that is significantly different from general-purpose X86 and X64 CPUs, as the command set for each protected file is different.
VMProtect supports almost all executable formats
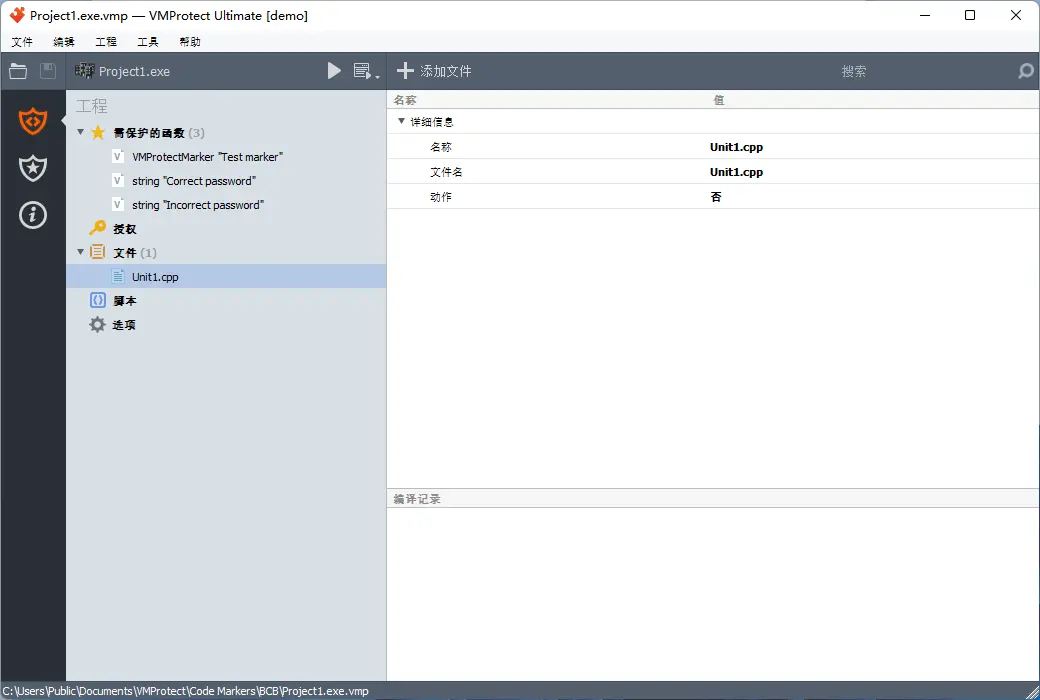
VMProtect allows protection of executable files (EXE, SCR), dynamic link libraries (DLL, OCX, BPL), and drivers (SYS). You can use the same protection for applications, their plugins, and even drivers!
3. VMProtect supports 64 bit code
Due to the increasing number of 64 bit systems, encryption programs must support them. We added support for 64 bit applications, libraries, and drivers in 2007, so everything has been well tested and you can easily migrate to 64 bit.
4. VMProtect supports most versions of Windows
Unlike some competitors, VMProtect does not rely on undocumented Windows features, so protected files can run well on almost any version of Windows system, even starting from Windows 95, and support 32-bit and 64 bit versions without DEP or UAC issues.
5. VMProtect is a complete protection solution
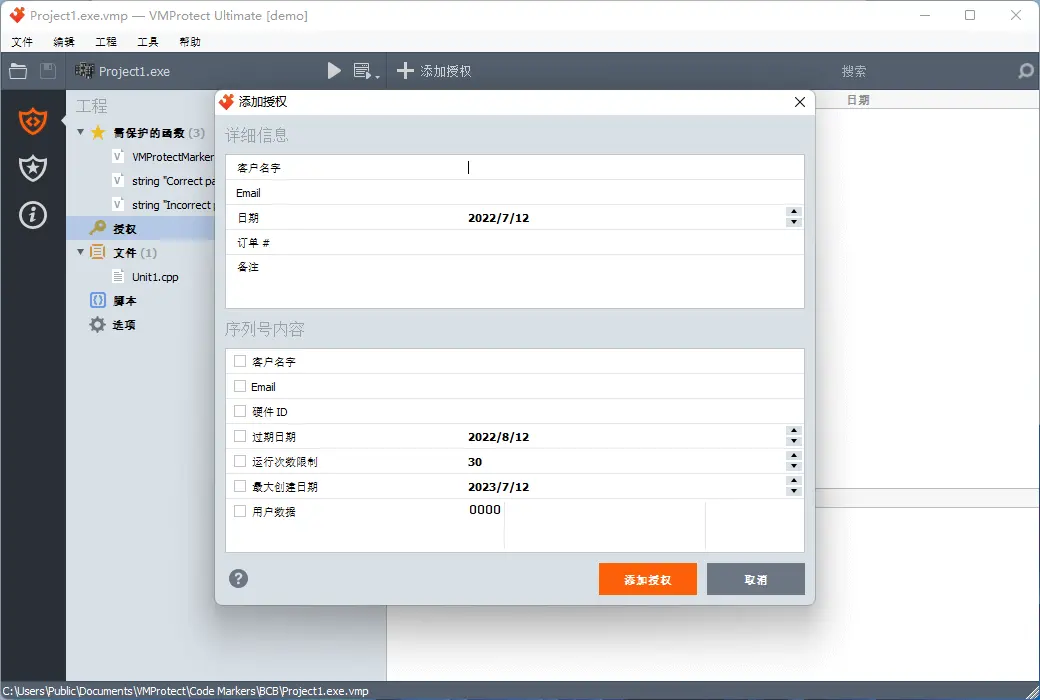
VMProtect allows for the generation and validation of serial numbers. Supports manual and automatic generation. The serial number may be limited by time or date and locked to hardware, and the free upgrade period may also be restricted. VMProtect ensures that running code without a serial number is physically impossible.
Official Website:https://vmpsoft.com/
Download Center:https://vmprotect.apsgo.cn
Delivery Time: Manual processing
Operating Platforms: Windows, macOS, Linux
Interface Language: Supports Chinese interface display, with multiple languages available.
Update Instructions: After purchase, support for updates and upgrades is provided for 1 year. After 1 year, a maintenance package can be purchased for further updates and upgrades.
Trial Before Purchase: Free trial is available before purchase.
How to Receive the Product: After purchase, activation information will be sent to the email address used for the order. Additionally, the corresponding product activation code can be viewed in the personal center, under "My Orders".
Number of Devices: Can be installed on 1 computer.
Changing Computers: Uninstall on the original computer and activate on the new computer.
Activation Guide: To be added.
Special Instructions: Please download the demo version for functional testing to ensure it meets your needs. The demo version cannot be used for registration.
Reference Materials:https://vmpsoft.com/support/faq/
Any question
Software products can be analyzed through static or dynamic analysis
Static analysis involves analyzing protected crack algorithms based on disassembly results or decompiling protected applications. Dynamic analysis is a necessary means to crack encrypted or dynamically changing executable files, as static analysis of such programs proves difficult
For dynamic analysis, the cracked program is executed within a debugger framework
In this way, everything that happens during the program's execution can be controlled by the debugger. During dynamic analysis, crackers use debug mode to bypass all protection algorithms in the program one by one, especially the registration key generation and checking process
Another commonly used tool for dynamic analysis is to track the files, system services, ports, and external devices queried by the cracked program
The main tool for protecting applications from cracking attempts is a software protector. Most protectors provide protection based on the packaging and/or encryption of the original executable file, with a focus on protecting the unpacking/decryption process
Such algorithms are often insufficient to provide reliable protection
If an application is protected by packaging, hackers can immediately perform a memory dump after the unpacker completes its work, immediately obtaining the original unpacked file
In addition, there are various automated tools that can crack the most popular protectors
The same goes for encryption: after obtaining a legitimate license key (usually purchased legally), crackers can decrypt the protected code sections
Some software protectors use multiple anti-debugging techniques, however, each factor significantly affects the performance of the protected project
Moreover, anti-debugging methods are only effective for dynamic analysis and completely ineffective for static analysis
Furthermore, all anti-debugging methods used by modern protectors are widely known and studied, and crackers have programmed many tools to circumvent or bypass these methods. Activity monitors are completely unaffected by built-in anti-debugging protections
A more effective method for protecting applications is obfuscation and virtualization, which complicates the analysis of protected application code
Generally, the efficiency of these protection methods depends on human factors: the more complex the code, the more resources the application consumes, and the harder it is for crackers to understand the program logic, making it more difficult to crack the protection
Obfuscation entangles application code by adding excessive instructions to the application, while virtualization converts source code into bytecode executed by a specific interpreter that simulates a virtual machine to execute specific commands
Therefore, virtualization results in high and non-simplifiable complexity in the final code. If applied properly, code protected by such methods does not contain explicit methods to restore the original code
Thus, the main advantage of virtualization is that virtualized code segments are not translated into machine language commands during execution, which in turn prevents crackers from obtaining the application's original code
The reverse engineering of virtualized segments is simplified to analyzing the virtual machine architecture, building an virtual machine to emulate the processor's corresponding architecture in an assembler, and analyzing the disassembled code